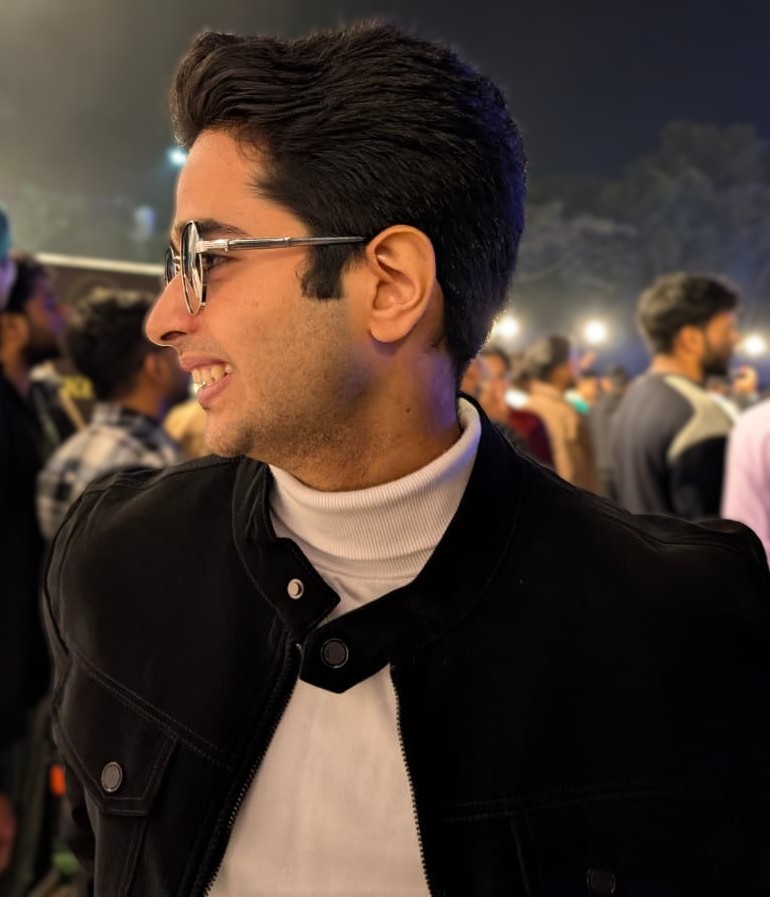
ABOUT ME / THE PERSON BEHIND THE PROJECTS

Hi, I’m Namitesh.

A quick introduction to what I’m learning and building.

01 / PROFILE
Namitesh Pandey
MEET THE CREATOR

Namitesh Pandey

Cybersecurity enthusiast

LEARNING BY BUILDING

Curiosity, backed by evidence.

I’m building practical security tools while learning how to investigate evidence, explain findings, and respect privacy.

Email securityWindows event logsDefensive triage
02FEATURED PROJECTS
LocalBROWSER-BASED TOOLS
HumanIN THE LOOP
DEFENSIVE SECURITY + PRACTICAL PROJECTS

Hi, I’m Namitesh ✳

Curious minds.
Thoughtful tools.

Exploring cybersecurity through practical tools that make evidence easier to understand.

NPPROJECTS BY NAMITESH PANDEYLEARN. BUILD. SHARE.
DEFENSIVE SECURITY✳EMAIL TRIAGE✳EVENT ANALYSIS✳HUMAN-LED INVESTIGATION✳
SKILLS IN CONTEXT

What I’m practising.

SELECT A SKILL TO EXPLORE THE PROJECT
SELECTED WORK / 2026

Projects with purpose.

Tools for email triage and Windows event investigation.

THE COLLECTION02 / 02
SHOWING 02 PROJECTSEXPLORE EACH PROJECT FOR MORE
/ 01Email securityComplete

Phishing Email Analyser.

An explainable email triage tool that turns suspicious signals into evidence you can review.

JavaScriptLocal analysisExplainable scoring
Explore project details
UNDER THE HOOD

Explore the details.

OPEN A SECTION TO LEARN MORE
Features3 highlights
  • Reviews message text, supplied headers, and captured link destinations.
  • Shows triggered rules, evidence coverage, and a capped 0–100 triage score.
  • Runs in the browser and offers redacted reports for careful sharing.
Algorithms & methods2 methods
Rule-based scoring

Adds fixed points for observed indicators; the result is a triage signal, not a probability.

Header & URL checks

Looks for supplied authentication results, sender mismatches, deceptive domains, and other visible clues.

Limitations
  • A low score cannot prove a message is safe; legitimate messages can also trigger rules.
  • Does not open links, inspect attachment contents, verify authentication cryptographically, or query live reputation.
Real-world applications
  • Practising phishing awareness
  • Prioritising messages for independent review
  • Learning how email indicators contribute to a score
README highlights
  • Three input modes: visible text, copied rich email, and raw source.
  • Evidence coverage is shown alongside the score.
  • No email content is sent to a backend or AI service for analysis.
Viva questions3 questions
01
Is this a machine-learning classifier?

No. It uses visible, fixed rules and point values to explain why an email deserves a closer look.

02
Does a low score prove an email is legitimate?

No. Missing evidence or unrecognised tactics can hide risk; verify important requests through a trusted channel.

03
How is privacy protected?

Analysis runs locally in the browser. The tool does not upload the email or visit extracted links.

Release notes
Version not specifiedPROJECT SOURCE
  • The current repository contains the latest documented implementation.
  • Release information can be added here when available.
View source
Presentation materials

Presentation materials have not been added for this project yet.

/ 02Log analysisComplete

Windows Security Event Log Triage Tool.

A local investigation workspace that helps analysts follow activity across Windows event exports.

JavaScript23 visible rulesMITRE ATT&CK
Explore project details
UNDER THE HOOD

Explore the details.

OPEN A SECTION TO LEARN MORE
Features3 highlights
  • Investigates authentication, account changes, process activity, services, and more.
  • Combines up to 20 export files with source tracking and conservative duplicate handling.
  • Includes coverage notes, case saving, analyst notes, and printable reports.
Algorithms & methods3 methods
Explainable detection rules

23 visible rules identify patterns and show supporting records, score contributions, and data gaps.

Evidence fingerprinting

SHA-256 fingerprints record the original bytes of source files locally.

ATT&CK context

Selected references support learning and investigation; they do not confirm a technique or change the score.

Limitations
  • Findings are leads for review, not proof of compromise or authorisation.
  • Results depend on available logs, timestamps, fields, and audit coverage. Raw EVTX requires local conversion.
Real-world applications
  • Learning Windows event analysis
  • Initial triage of authorised exports
  • Organising evidence for a human-led investigation
README highlights
  • Accepts CSV, Windows Event XML, JSON, and JSON Lines exports.
  • Source fingerprints, evidence references, and coverage gaps stay visible.
  • Logs are processed locally without automatic upload or storage.
Viva questions3 questions
01
What does a finding prove?

It highlights activity for investigation; context and additional evidence are needed before drawing a conclusion.

02
Why record SHA-256 fingerprints?

They provide an identifier for the original source-file bytes, helping an analyst track evidence provenance.

03
Why show coverage gaps?

Missing event types or fields can prevent a rule from being assessed, so no finding is not proof that nothing happened.

Release notes
v1.7.0UNRELEASED IN CHANGELOG
  • Source-file fingerprints and ATT&CK learning references.
  • Printable investigation reports and evidence provenance.
View source
v1.6.0PREVIOUS VERSION
  • Multi-file investigations and per-rule coverage.
  • Source tracking and conservative duplicate detection.
View source
Presentation materials

Presentation materials have not been added for this project yet.

THE WORKFLOW / INTERACTIVE

See how it works.

Follow the evidence through each project, one step at a time.

02 / PROCESS
CHOOSE A PROJECT

Phishing Email Analyser

Follow the journey from a suspicious message to an explainable assessment.

01✳
EVIDENCE INPUT

Collect the evidence.

Paste message text, copied rich email, or raw email source for local analysis.

KEEP IN MIND

Headers and links provide extra context when they are available.

THE APPROACH

Build. Question.
Keep learning.

I’m interested in tools that make their reasoning visible, respect the evidence, and leave room for human judgment.

PRACTICAL LEARNING EXPLAINABLE IDEAS HONEST LIMITS
ALWAYS LEARNING, ALWAYS BUILDING

Thanks for stopping by.

Explore the code and follow the next chapter on GitHub.

Visit my GitHub